 CallScope by Belton
Identity and access
Microsoft Entra ID single sign-on, two-factor for administrators, and role-based access enforced on the server, deny by default.
Agencies are judged on how they answer the public. CallScope gives your contact centre live operational insight, and gives your security, privacy and audit teams the controls and evidence a public-sector procurement expects.
Microsoft Entra ID single sign-on, two-factor for administrators, and role-based access enforced on the server, deny by default.
Append-only, hash-chained audit log, a printable audit report and optional SIEM export.
Onshore hosting in New Zealand or Australia, or inside your own environment.
Off by default, onshore options, offshore services blocked, and a person always in the loop.
Card numbers stripped from transcripts, sensitivity tiers, retention with daily purge, and erasure on request.
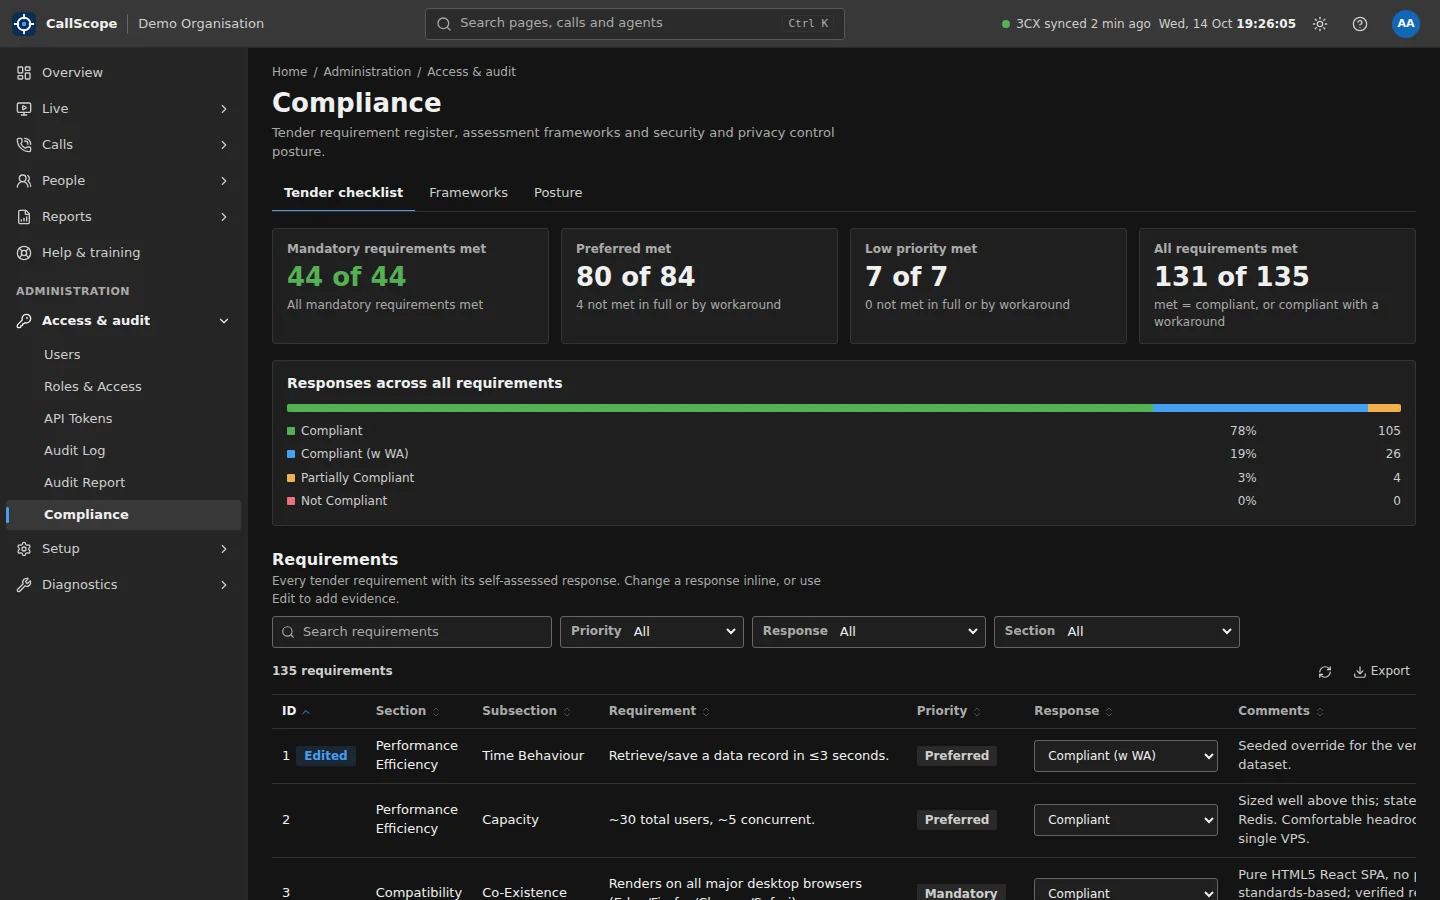
A built-in compliance register and control mapping to NZISM, Essential Eight and ISO 27001.
The built-in compliance register tracks tender requirements and framework controls, and the audit report gives assessors a live view of the evidence.
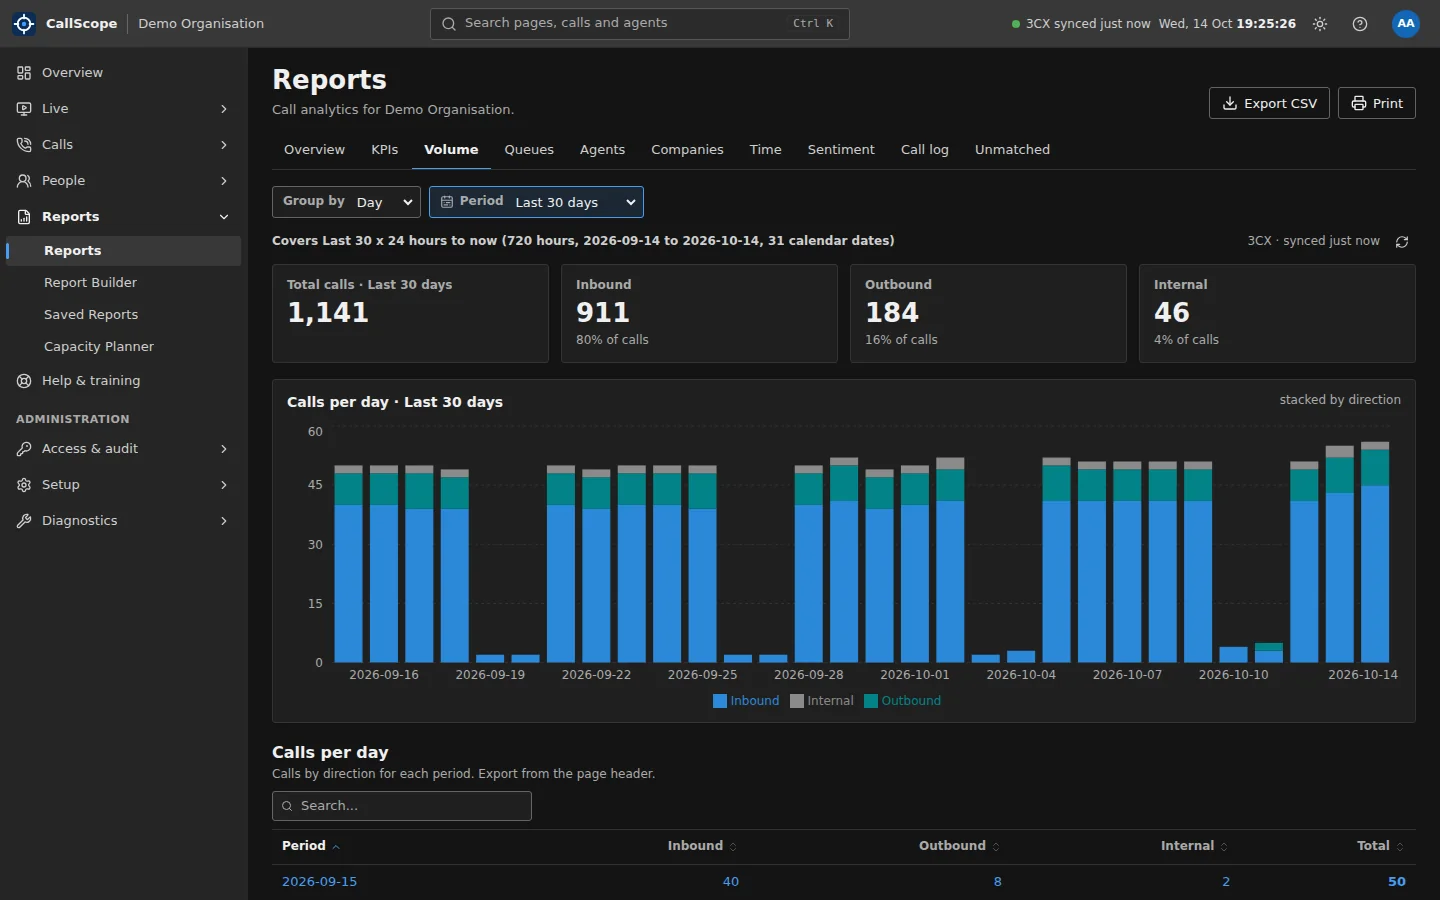
Service level, speed of answer, abandonment and first-contact resolution, by queue and period, with every figure traceable to the calls it counted.
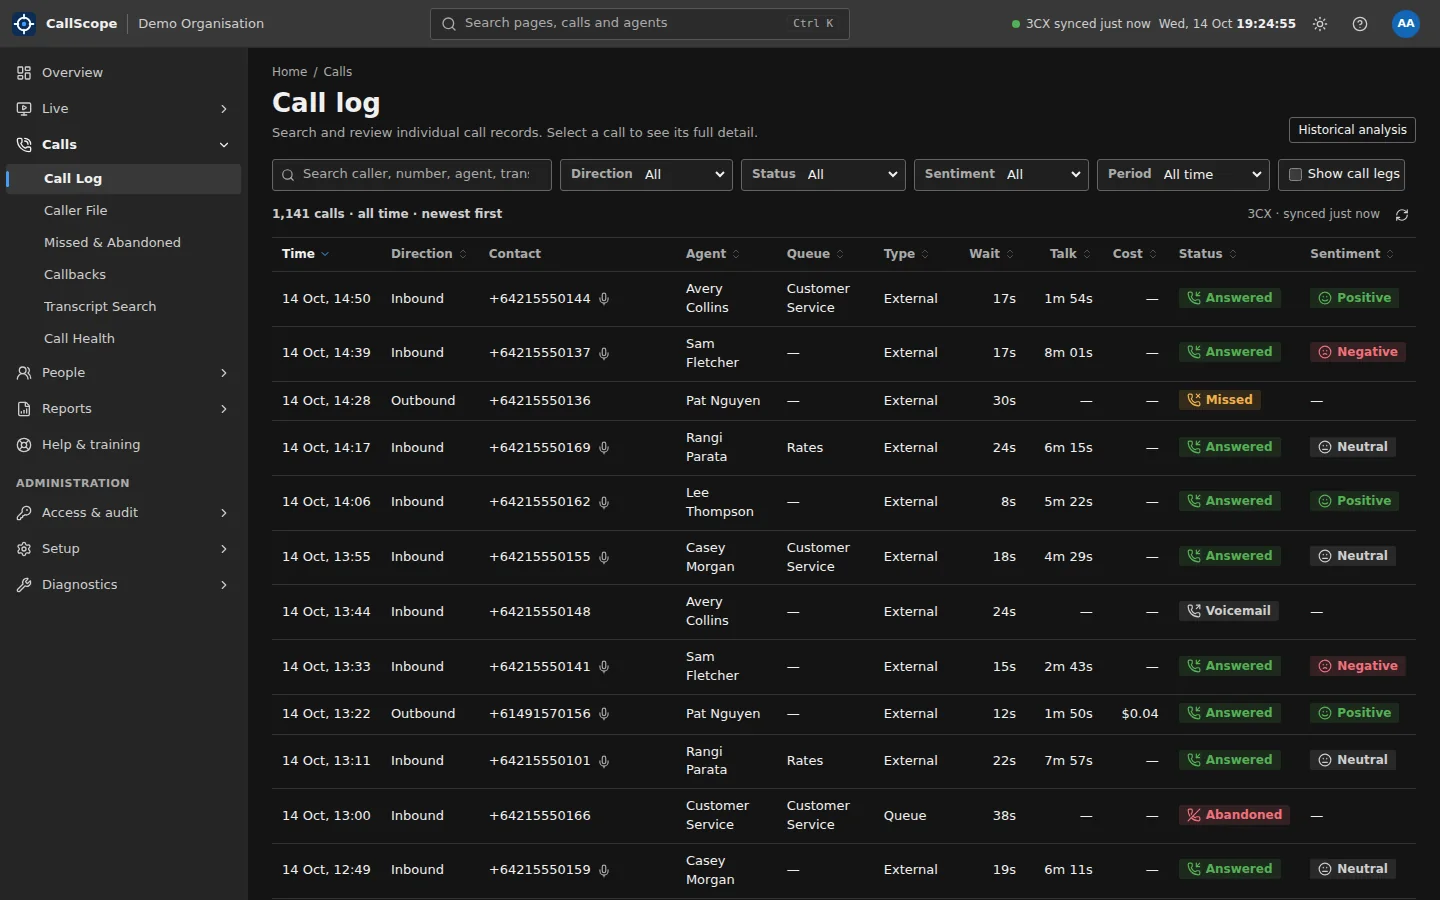
Calls rolled up from 3CX segments into the calls people actually made, filterable, exportable and searchable, with recording playback audited.
We tell you exactly what is in place, what is in progress and what is not held. No overclaiming.
Self-host inside your own environment, or use an onshore Belton instance.
Nightly AES-256 encrypted backups with an optional immutable offsite copy.
Scoped, expiring read tokens with rate limits and an OpenAPI specification.
CallScope never changes your 3CX routing, queues or extensions.
No. CallScope is designed around the controls in ISO 27001, NZISM and the Essential Eight, and Belton has self-assessed against them. We do not claim certifications we do not hold. During procurement we give you the control mapping and tell you exactly what is in place, in progress and not held.
Yes. CallScope runs as a standard container stack on your own servers and network. For highly sensitive or isolated networks we scope a deployment with no outbound services, and AI features stay off or use a model you host.
AI is off by default. When enabled you choose the provider: Belton's own self-hosted model, a model you host, or Azure OpenAI in Australia. Offshore AI services are blocked in code unless the deployment explicitly allows them. AI findings are inputs for a person to review, never automatic actions, and AI output that fails validation is refused and audited.
Yes. The audit log can be shipped as RFC 5424 syslog over TCP or TLS every few minutes, or pulled as NDJSON. Within CallScope the log is append-only and hash-chained, with a one-click integrity check and a printable audit report.
Tell us about your environment and your assurance requirements, and we will show you how CallScope meets them.